In pursuit of greatness
curriculum vitæ

Saïd S.
on my way to the SOC

Three years in IT. Two of them inside the systems and networks of a CAC 40 energy giant. I invested serious hours into CTFs, which gave me the attacker perspective first, then the SOC became the field I chose to build in. Based in Lyon, open to France and the UK first, then the rest of Europe.
Departure
IT support, 2022
Stops so far
4 companies, 1 master's degree in cybersecurity
Experience
3 years in IT
Destination
SOC analyst N1, January 2027
the route
Sep 2022 → Sep 2023
i-Tech
IT technician
First experience. Server administration and maintenance, alongside the security side of the role. Set up and secured firewalls with IPS/IDS and network interface configuration, ran vulnerability scans, access control and system hardening, and delivered cybersecurity awareness lectures in high schools.
firewallsIPS/IDSvulnerability scanshardeningsupport
Sep 2023 → Dec 2023
Mairie de Perpignan
Systems, Networks & Security Admin
A few months in public sector IT. Handled system upgrades from patch deployments to software dependency management, daily backups with retention policies and integrity checks, secured IT profiles and assets, and ran basic intrusion testing on database servers, then addressed what it found. Kept the Bash, PowerShell and Python automation scripts alive and wrote the update reports to go with them.
patchingbackupsintrusion testingBashPowerShellPython
2023 → 2026
Relevant coursesWeb Pentesting · Malware Analysis & Detection · Reverse Engineering · Incident Detection & Response · Digital Forensics · Network Security
EPITECH
Master degree Cybersecurity, GPA 3.8 / 4.0
The degree pursued alongside professional roles. Three years, with cybersecurity as the specialisation and strong academic results.
Master degreecybersecurityGPA 3.8
Jan 2024 → Aug 2024
COULEUR'
Full-stack developer
Eight months building web applications end to end for real clients. Front-end and back-end features primarily in PHP, translating client needs into technical specifications, handling client requests and resolving issues, unit and integration testing, and continuously improving the existing applications.
PHPfront-endback-endtesting
Sep 2024 → Sep 2026
TotalEnergies
Systems, Networks & Security Admin (apprenticeship)
Two years inside the IT of a CAC 40 energy giant. Built and tested IoT systems with a focus on security, ran security assessments and network exposure testing, deployed Zabbix monitoring which improved incident detection by 70 percent, automated tasks in Bash cutting manual workload by 30 percent, led security awareness sessions with simulated phishing, vishing and CEO-fraud exercises, took part in a cyber crisis simulation, and managed users and access rights for sensitive industrial zones. This is where the focus shifted, from offensive curiosity to detection and incident response.
Zabbixsecurity assessmentsIoTBashawarenessaccess rights
Now
In parallel: launching applications and SaaS projects, hackathons and CTFs, organised around the certification schedule.
Current position
Finishing the apprenticeship, focused on certifications and the job search
SOC analyst path in progress. Daily LetsDefend, SC-200 in October, BTL1 in November, home lab running in Docker, CTFs on weekends. Available from October.
LetsDefendhome labavailable
Oct 2026
SC-200
Microsoft Security Operations Analyst
Sentinel and Defender, the stack I want to run in production.
Nov 2026
BTL1
Blue Team Level 1
Hands-on blue team work. Phishing triage, SIEM queries, practical validation.
Jan 2027
Security+
CompTIA Security+
The certification recruiters filter on. In progress.
Jan 2027
SOC Analyst N1
the destination
Full time detection and response. That is the plan.
receipts
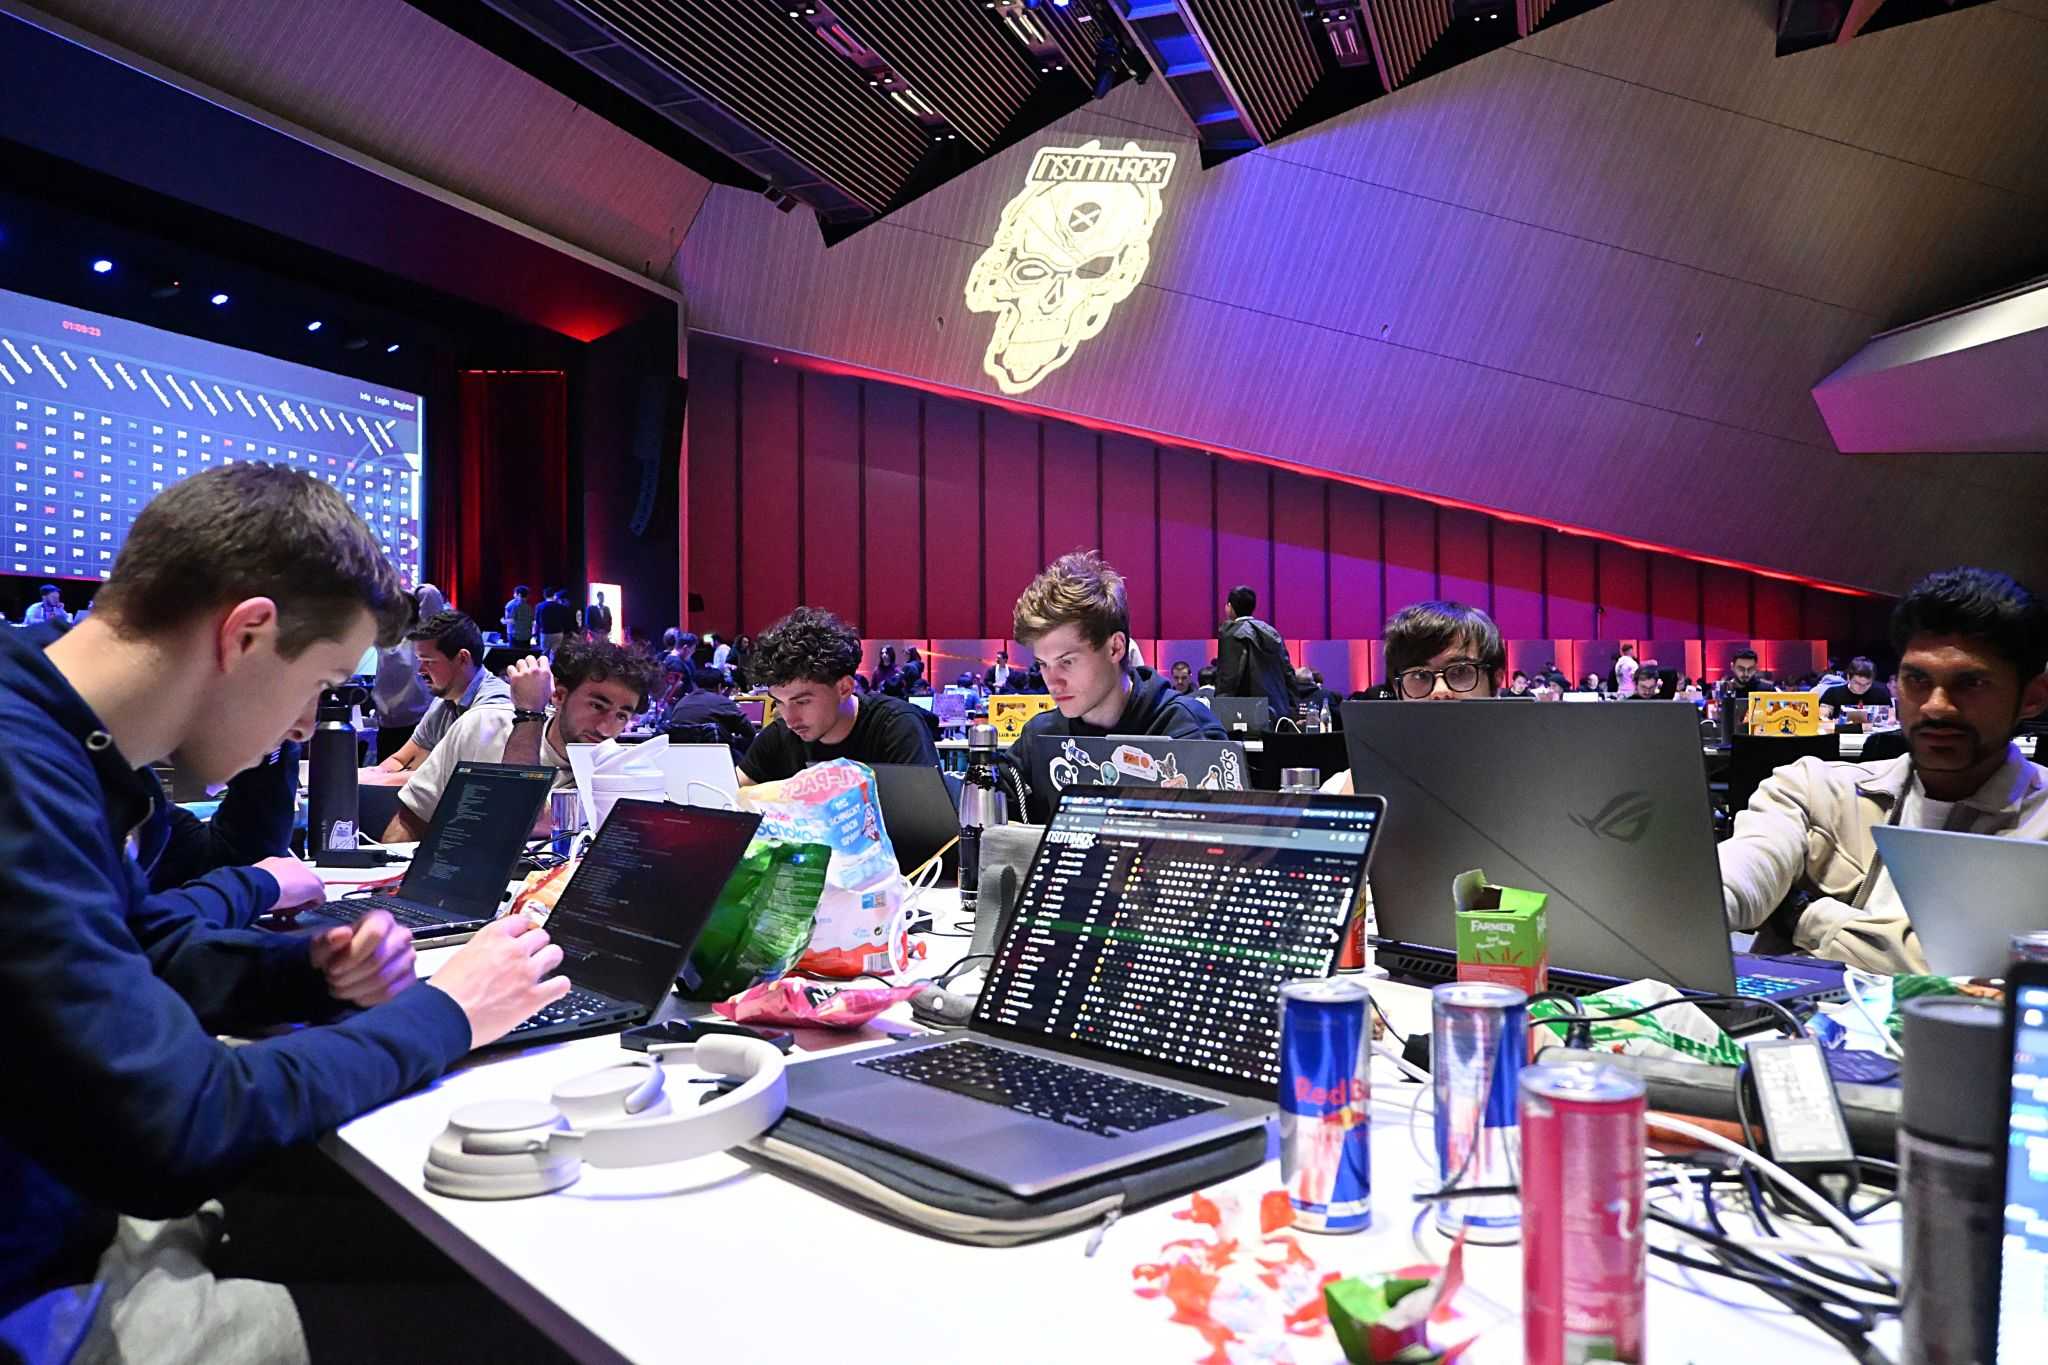
Insomni'Hack 2026 venue and scoreboard
22/116
Insomni'Hack 2026, Geneva. First international CTF, top academic team.
3rd
POC CTF 2025, overall. First place in web security, 6000+ students.
950
TOEIC. Fully operational in professional English.
350h+
HackTheBox. The foundation of the offensive skill set.
6th
Cyber 9/12. Strategy and incident response under pressure, team event.
the arsenal

SOC & detection

  • Splunk daily driver
  • Microsoft Sentinel solid
  • Wazuh solid
  • CrowdStrike basics
  • Wireshark solid
  • Volatility basics

Offensive

  • Nmap solid
  • Burp Suite solid
  • Web exploitation CTF level
  • Binary exploitation learning
  • OSINT solid

Ops & systems

  • Windows & AD admin 2 years pro
  • PowerShell admin level
  • Bash / Linux daily
  • Python working knowledge
  • Docker labs & tools
things I built

HumanLayer

Voice liveness API. A challenge phrase and a microphone instead of iris scans. Built in five days for the YC RFS.

PythonWhisper · Silero VAD

scrim analytics platform

Esports analytics platform. Upload end game screenshots, GPT-4o Vision parses them, the coach gets reliable winrate data.

Next.js~24k lines

RiftRank

Discord bot and web app for community League tournaments. Rank checks, brackets, leaderboards. Beta while the Riot API review runs.

Discord.pyweb app

gemini live tutor

Realtime voice tutor on the Gemini Live API. Ephemeral tokens, function calling, interruption handling. Built as a daily study tool.

Pythonaiohttp

s0p0wn3d C2

A command and control framework built from scratch, ECDH and AES-GCM included, to learn what the other side actually looks like on a SOC console.

C++Django

usb ghost

Physical access assessment toolkit. Demonstrates that browsers cannot protect session cookies from a local admin. Released after a full secrets audit of the repository.

BatchPowerShell

soc lab

Home SOC in Docker. Elasticsearch, Sysmon, a simulated corporate network and a Kali box on a schedule. Notes in French so the whole environment can be rebuilt from them.

ElasticTheHive

from log to case

One brute force in my own lab, walked end to end. The failed logins, the queries that name the attacker, and the case that closes it.

SplunkTheHive

cyber hub

Daily security quiz with explanations, SOC cheatsheets, live CVEs and translated news. My revision loop, one question at a time.

Cloudflare Pagesstatic PWA

discord sniping bot

24/7 monitor for French TCG marketplaces. Price drops, price errors, restocks, straight to Discord.

Pythonasyncio · curl_cffi

soc job dashboard

Pipeline that scrapes junior SOC offers across France and the UK, scores them against my profile with an LLM, and serves them in a dashboard with application tracking.

Cloudflare PagesD1 · LLM scoring
Looking for an ambitious SOC team, a real stack to master, Splunk or Sentinel. Available from October.

The long version of some of these projects is on the blog.